Digital Information Governance vs Data Governance: Key Differences
Data governance manages your data; Digital Information Governance® (DIG) governs the AI-influenced decisions made from it. How they differ and why AI regulation requires governing the decision.
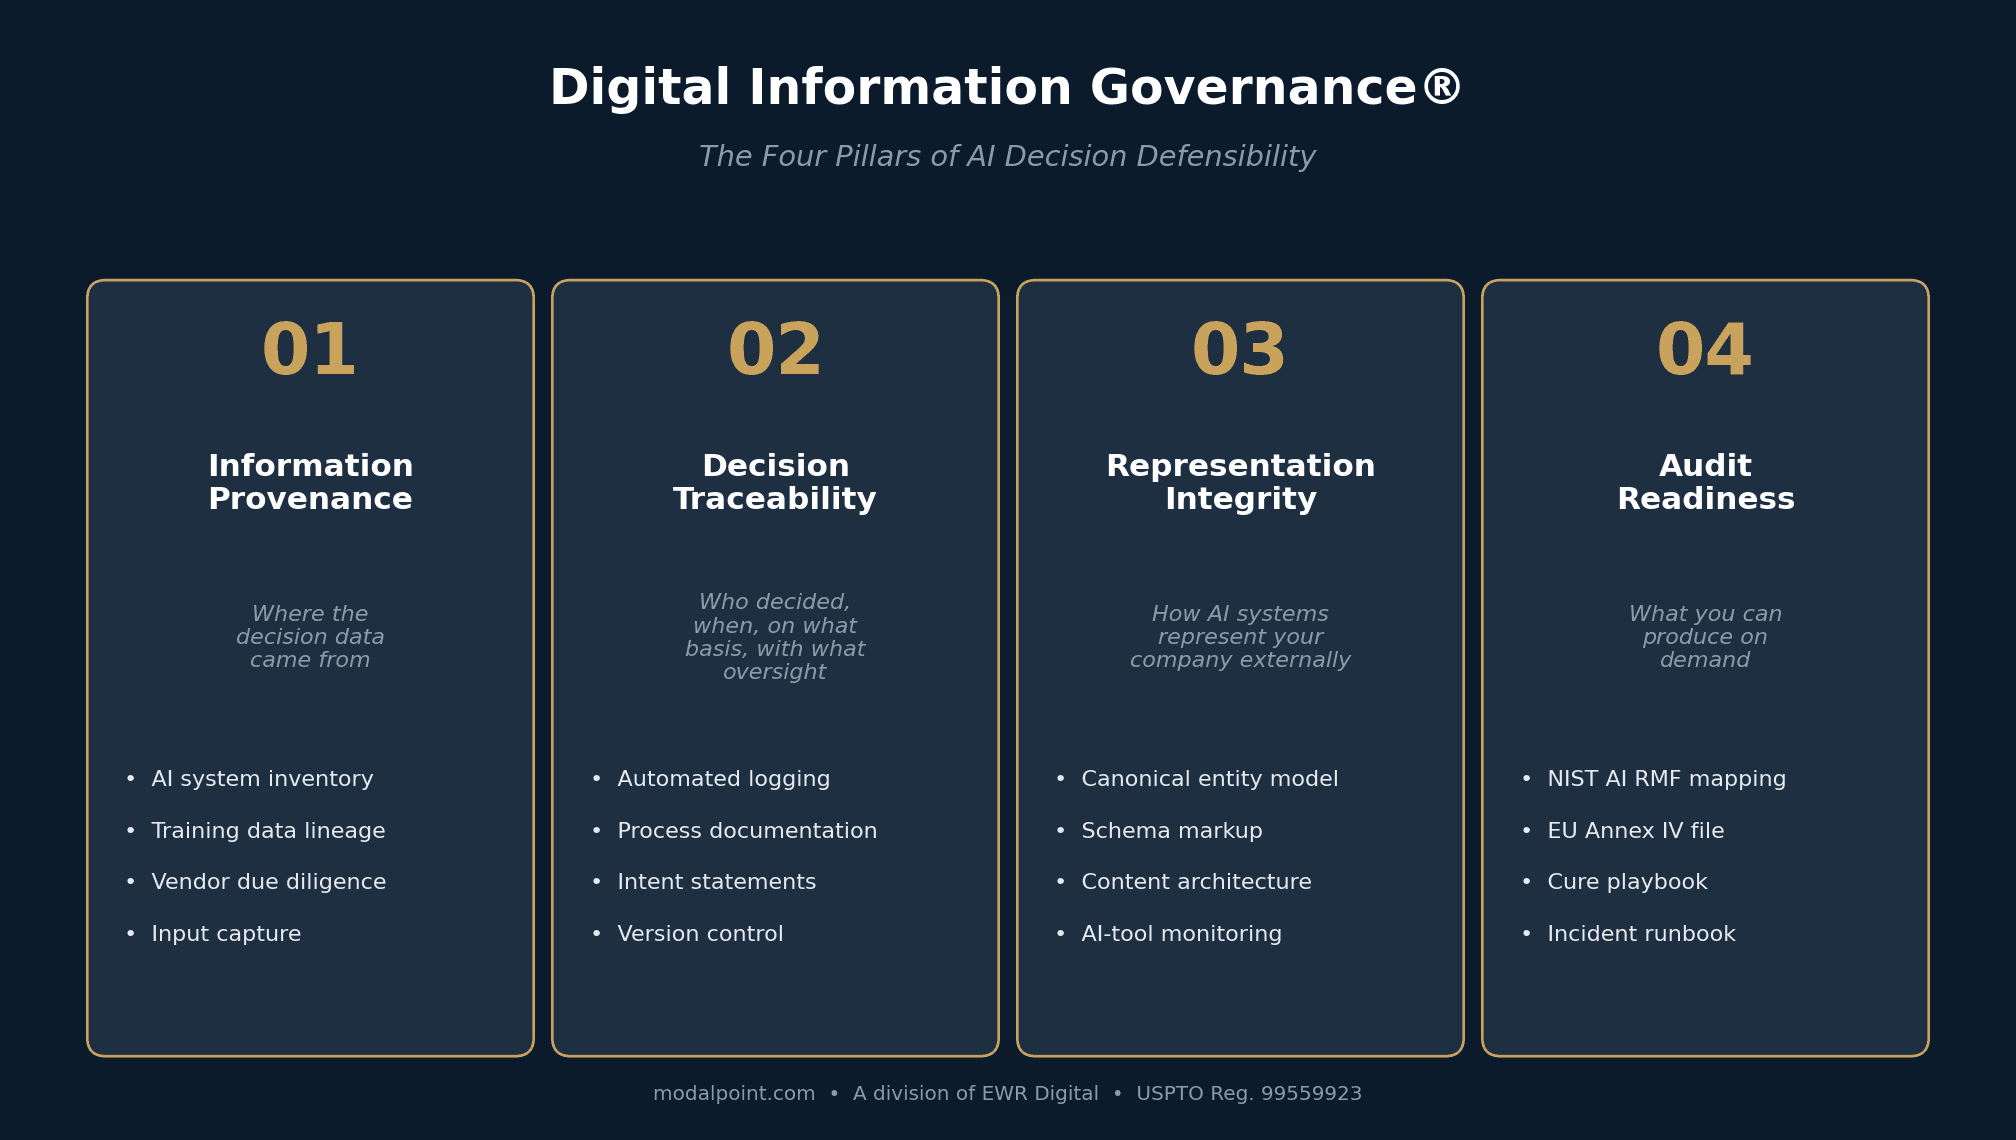
Digital Information Governance vs Data Governance
Last updated: June 2026 · ModalPoint
Data governance manages your data; Digital Information Governance® (DIG) governs the AI-influenced decisions made from it. Data governance keeps data accurate, secure, and usable across its lifecycle. Digital Information Governance is the AI-era layer on top — it makes the decisions an AI system influences documented, accountable, and defensible to a regulator, board, or auditor. They are complementary, not competing: good data governance is a precondition; DIG is what proves the resulting decisions were safe.
The distinction matters more every quarter. In McKinsey’s 2025 survey, 88% of organizations reported using AI in at least one function, yet only about 6% capture enterprise-wide value — and in energy, roughly 86% of AI projects never leave the pilot stage. The blocker is rarely data quality. It is the inability to show how an AI-influenced decision was made, who owned it, and why it was defensible. That gap is what Digital Information Governance closes — and it is why a discipline built for data is not the same as one built for AI decisions.
Data governance vs information governance vs Digital Information Governance
Three terms get used interchangeably and shouldn’t be. Each governs a different thing, emerged in a different era, and produces a different artifact.
| Dimension | Data Governance | Information Governance | Digital Information Governance® (DIG) |
|---|---|---|---|
| What it governs | The data itself — quality, lineage, access, security | Information as an asset — records, retention, privacy, legal/e-discovery | The AI-influenced decision — how AI shapes it and whether it’s defensible |
| Core question | “Is our data accurate, secure, and usable?” | “Are we managing information per policy and law?” | “Can we prove how this AI-influenced decision was made, and who is accountable?” |
| Era / driver | Big data, cloud, BI (2000s–) | Compliance, records, e-discovery (1990s–) | AI regulation: TRAIGA, EU AI Act, NIST AI RMF (2024–) |
| Primary artifact | Data catalog, quality rules, access policy | Retention schedule, privacy policy, records inventory | Decision Audit Report — inputs, model version, reviewer, rationale |
| Owner | Chief Data Officer / data teams | Legal, compliance, records management | A named decision owner, with board/audit accountability |
What is data governance?
Data governance is the set of principles, policies, and processes that keep an organization’s data accurate, secure, available, and usable across its lifecycle. It covers data quality, metadata and lineage, master data management, access controls, and regulatory compliance — typically owned by a Chief Data Officer or data-management function. Its goal is trustworthy data as a strategic asset.
Data governance is mature and essential. But it answers a question about data, not about decisions. It can certify that the dataset feeding a model is clean and well-governed, and still tell you nothing about whether the AI recommendation built on that data was reviewed, documented, or defensible. In an AI-driven operation, that’s the gap that creates risk.
What is information governance?
Information governance is broader than data governance. It is the framework of accountability and decision rights for managing information as a whole — records management, retention and disposal, privacy, security classification, legal hold, and e-discovery readiness. Where data governance is data-team-led, information governance is usually a multidisciplinary effort spanning legal, compliance, records, and IT.
Information governance asks whether you are handling information correctly under policy and law. It still predates the central problem of the AI era: not whether information is managed, but whether the decisions AI makes with it can be explained and defended.
What is Digital Information Governance® (DIG)?
Digital Information Governance® (DIG) is ModalPoint’s framework for AI decision defensibility — protected as a registered U.S. trademark (USPTO Reg. No. 8147558) with three provisional patents filed. It governs the AI-influenced decision itself: it captures the inputs, model version, human reviewer, and rationale behind each material decision and retains them as evidence, so the resulting record maps onto TRAIGA, the EU AI Act, the NIST AI RMF, and ISO/IEC 42001 at once.
DIG does not replace data governance — it sits above it. Data governance ensures the inputs are trustworthy; DIG ensures the AI-influenced decision built on them is documented, accountable, and defensible. The deliverable is a Decision Audit Report: a regulator-ready record of how a high-stakes AI-influenced decision was made. See the full AI decision governance framework →
Why does AI change what governance has to mean?
For decades, governance was about the asset: govern the data, govern the records, and you were covered. AI breaks that model because AI doesn’t just store information — it acts on it, shaping decisions about pricing, capital, safety, and compliance. A perfectly governed dataset can still feed an AI recommendation that no one can explain after the fact. When a regulator, board member, or auditor asks “how was this decision made, and who is accountable?”, a data catalog cannot answer. A Decision Audit Report can.
This is why the AI-regulation wave targets decisions and outcomes, not data hygiene. The Texas Responsible AI Governance Act (TRAIGA) opens its Attorney General complaint portal on September 1, 2026; the EU AI Act imposes risk-tiered obligations including logging and human oversight; the NIST AI RMF and ISO/IEC 42001 organize controls around governing AI risk. None of these are satisfied by data governance alone. They require governing the decision — which is what Digital Information Governance was built to do.
Which do you need — and in what order?
- Start with data governance if your data is unreliable, siloed, or insecure — AI built on bad data fails regardless of oversight.
- Add information governance for records, retention, privacy, and legal-hold obligations across the information lifecycle.
- Layer Digital Information Governance on top the moment AI starts influencing material decisions — especially in regulated or safety-critical operations. This is the layer regulators, boards, and auditors now ask about, and the one most organizations are missing.
Proof: governance applied to a dual-listed operator
Digital Information Governance is a production framework, not a concept. Applying DIG for Tamboran Resources (NYSE: TBN, ASX: TBN), ModalPoint moved the operator from effectively invisible to #1 across the core Beetaloo Basin AI queries in 60 days — 100% of monitored core search terms migrated into the Top 10, and the company went from misrepresented across six different LLMs to cited as the primary authority. It was named a 2026 AMA Houston Crystal Awards finalist in the AI category. Read the case study →
Frequently asked questions
What is the difference between data governance and Digital Information Governance?
Data governance manages the data itself — its quality, lineage, access, and security. Digital Information Governance® (DIG) governs the AI-influenced decisions made from that data, capturing the inputs, model version, reviewer, and rationale so the decision is documented, accountable, and defensible. Data governance is a precondition; DIG is the AI-era layer above it.
Is information governance the same as data governance?
No. Data governance focuses on data quality, security, and usability and is typically data-team-led. Information governance is broader — records, retention, privacy, and legal/e-discovery across the information lifecycle — and is usually led by legal, compliance, and records functions. Both predate the AI-decision problem that Digital Information Governance addresses.
Does Digital Information Governance replace data governance?
No — it sits on top of it. Data governance ensures the inputs are trustworthy; DIG ensures the AI-influenced decisions built on those inputs are defensible to a regulator, board, or auditor. You need both: clean data alone does not make an AI decision auditable.
Why isn’t data governance enough for AI compliance?
Because AI regulation targets decisions and outcomes, not data hygiene. TRAIGA, the EU AI Act, the NIST AI RMF, and ISO/IEC 42001 ask whether AI-influenced decisions are risk-classified, logged, human-overseen, and accountable. A data catalog can’t answer that. Governing the decision — the DIG approach — can.
Who coined Digital Information Governance?
Digital Information Governance® (DIG) is a framework created by Matt Bertram, CEO of ModalPoint. It is a registered U.S. trademark (USPTO Reg. No. 8147558) with three provisional patents filed, developed specifically for AI decision defensibility in regulated and safety-critical industries such as energy.
What does Digital Information Governance produce?
The core artifact is a Decision Audit Report — a regulator-ready record of how a high-stakes AI-influenced decision was made, capturing inputs, model version, human reviewer, and rationale. For multi-jurisdiction operators the registry maps to TRAIGA, the EU AI Act, the NIST AI RMF, and ISO/IEC 42001 so a single export satisfies multiple audit requests.
Do I need a Chief Data Officer or a decision owner?
Both serve different roles. A Chief Data Officer owns data governance — the quality and security of data. Digital Information Governance assigns a named decision owner accountable for a specific AI-influenced decision, so accountability never disappears into the model. The two are complementary.
How do energy companies apply this?
Energy operators run AI into decisions affecting safety, capital, and pricing across upstream, midstream, and downstream — often spanning enterprise IT and operational technology (OT). DIG governs those decisions across both domains, starting with a $2,500 Shadow AI Exposure Assessment to surface unsanctioned AI usage, then instrumenting the high-stakes decisions. See the framework →
Reviewed by Matt Bertram, CEO of ModalPoint — Certified AI Auditor (CAIA), creator of the Digital Information Governance® (DIG) framework, co-host of the Oil & Gas Global Network (OGGN), and OTC 2026 panelist, with 25+ years in energy commercialization.
Frequently asked questions
Why isn't data governance enough for AI compliance?+
Talk to ModalPoint
A 20-minute call to see if ModalPoint is the right firm and whether the timing makes sense. No obligation either way.