EU AI Act vs NIST vs ISO 42001 vs TRAIGA: How the Four AI Governance Frameworks Compare
The Oil and Gas Sales Experts. If you need to sell your product or service to the Oil and Gas industry, we can make it happen!
If you are trying to work out which AI rules actually force your company to act, here is the short version. The EU AI Act and New York City Local Law 144 are binding mandates with real penalties and, for some systems, a required independent audit. Texas TRAIGA is not a mandate at all: it is a safe-harbor incentive that rewards you for following the NIST AI Risk Management Framework. NIST AI RMF is a voluntary framework, and ISO/IEC 42001 is a voluntary standard you can be certified against. The table below compares all four on legal status, who they bind, penalties, and whether a third-party audit is required.
The four frameworks at a glance
| Framework | Legal status | Who it binds | Penalties | Third-party audit required? |
|---|---|---|---|---|
| EU AI Act | Binding law (mandate) | Providers and deployers whose AI output is used in the EU, worldwide | Up to 35M euros or 7% of global turnover (prohibited); 15M euros or 3% (high-risk / GPAI) | Yes for high-risk: notified-body conformity assessment |
| Texas TRAIGA (HB 149) | Safe-harbor incentive (with penalties) | Businesses using AI with Texas residents; state agencies | 10,000 to 12,000 dollars curable; 80,000 to 200,000 dollars uncurable; 2,000 to 40,000 dollars per day continuing | No mandate. NIST alignment earns a presumption of reasonable care |
| NYC Local Law 144 | Binding law (narrow mandate) | Employers using automated hiring tools on NYC candidates | 500 to 1,500 dollars per violation, per day | Yes: independent bias audit, annual, posted publicly |
| NIST AI RMF | Voluntary framework | Anyone; adopted by choice or by reference | None (not a law) | No |
| ISO/IEC 42001 | Voluntary, certifiable standard | Organizations seeking certification | None (market and procurement driven) | Yes if you pursue certification: accredited third-party audit |
EU AI Act: the broadest mandate
The EU AI Act is the world’s first comprehensive AI law, and it reaches any company whose AI system output is used inside the EU, wherever that company sits. Obligations phase in over time: banned practices took effect February 2, 2025, general-purpose AI model rules on August 2, 2025, and the core high-risk obligations on August 2, 2026. Penalties reach up to 35 million euros or 7% of global annual turnover for prohibited practices, and up to 15 million euros or 3% for most other violations. For high-risk systems, a notified-body conformity assessment is the real audit forcing function.
Texas TRAIGA: a safe harbor, not an audit mandate
The Texas Responsible Artificial Intelligence Governance Act (HB 149) takes effect January 1, 2026, and it is widely misread as an audit requirement. It is not. TRAIGA gives you a rebuttable presumption of reasonable care if you substantially comply with the NIST AI Risk Management Framework and run internal review. Civil penalties run from 10,000 to 12,000 dollars per curable violation, 80,000 to 200,000 dollars per uncurable violation, and 2,000 to 40,000 dollars per day for continuing violations. Only the Texas Attorney General can enforce it, there is no private right of action, and you get a 60-day window to cure. For why TRAIGA does not preempt federal civil-rights law, see our TRAIGA explainer.
NIST AI RMF: voluntary, but the reference everyone points to
The NIST AI Risk Management Framework is a voluntary US framework built on four functions: Govern, Map, Measure, and Manage. It carries no penalties of its own. Its power is by reference: the TRAIGA safe harbor is built on it, and it maps cleanly onto EU AI Act and ISO 42001 evidence. Adopt NIST first and everything downstream gets cheaper.
ISO/IEC 42001: voluntary, but certifiable
ISO/IEC 42001:2023 is the first international AI management-system standard, and unlike NIST you can be formally certified against it by an accredited body. There is no legal penalty for skipping it, but certification is increasingly a procurement requirement in enterprise and government deals. It is the closest thing to a portable, third-party-verified proof of AI governance.
NYC Local Law 144: the one true bias-audit mandate
If you use automated tools to screen or rank job candidates in New York City, Local Law 144 requires an independent third-party bias audit before you use the tool, renewed every year, with the results posted publicly and candidates notified. It is narrow (employment only) and enforcement has been light, but it is the clearest example in the US of a law that actually requires an outside audit. Penalties run 500 to 1,500 dollars per violation, per day.
One system of record satisfies all four
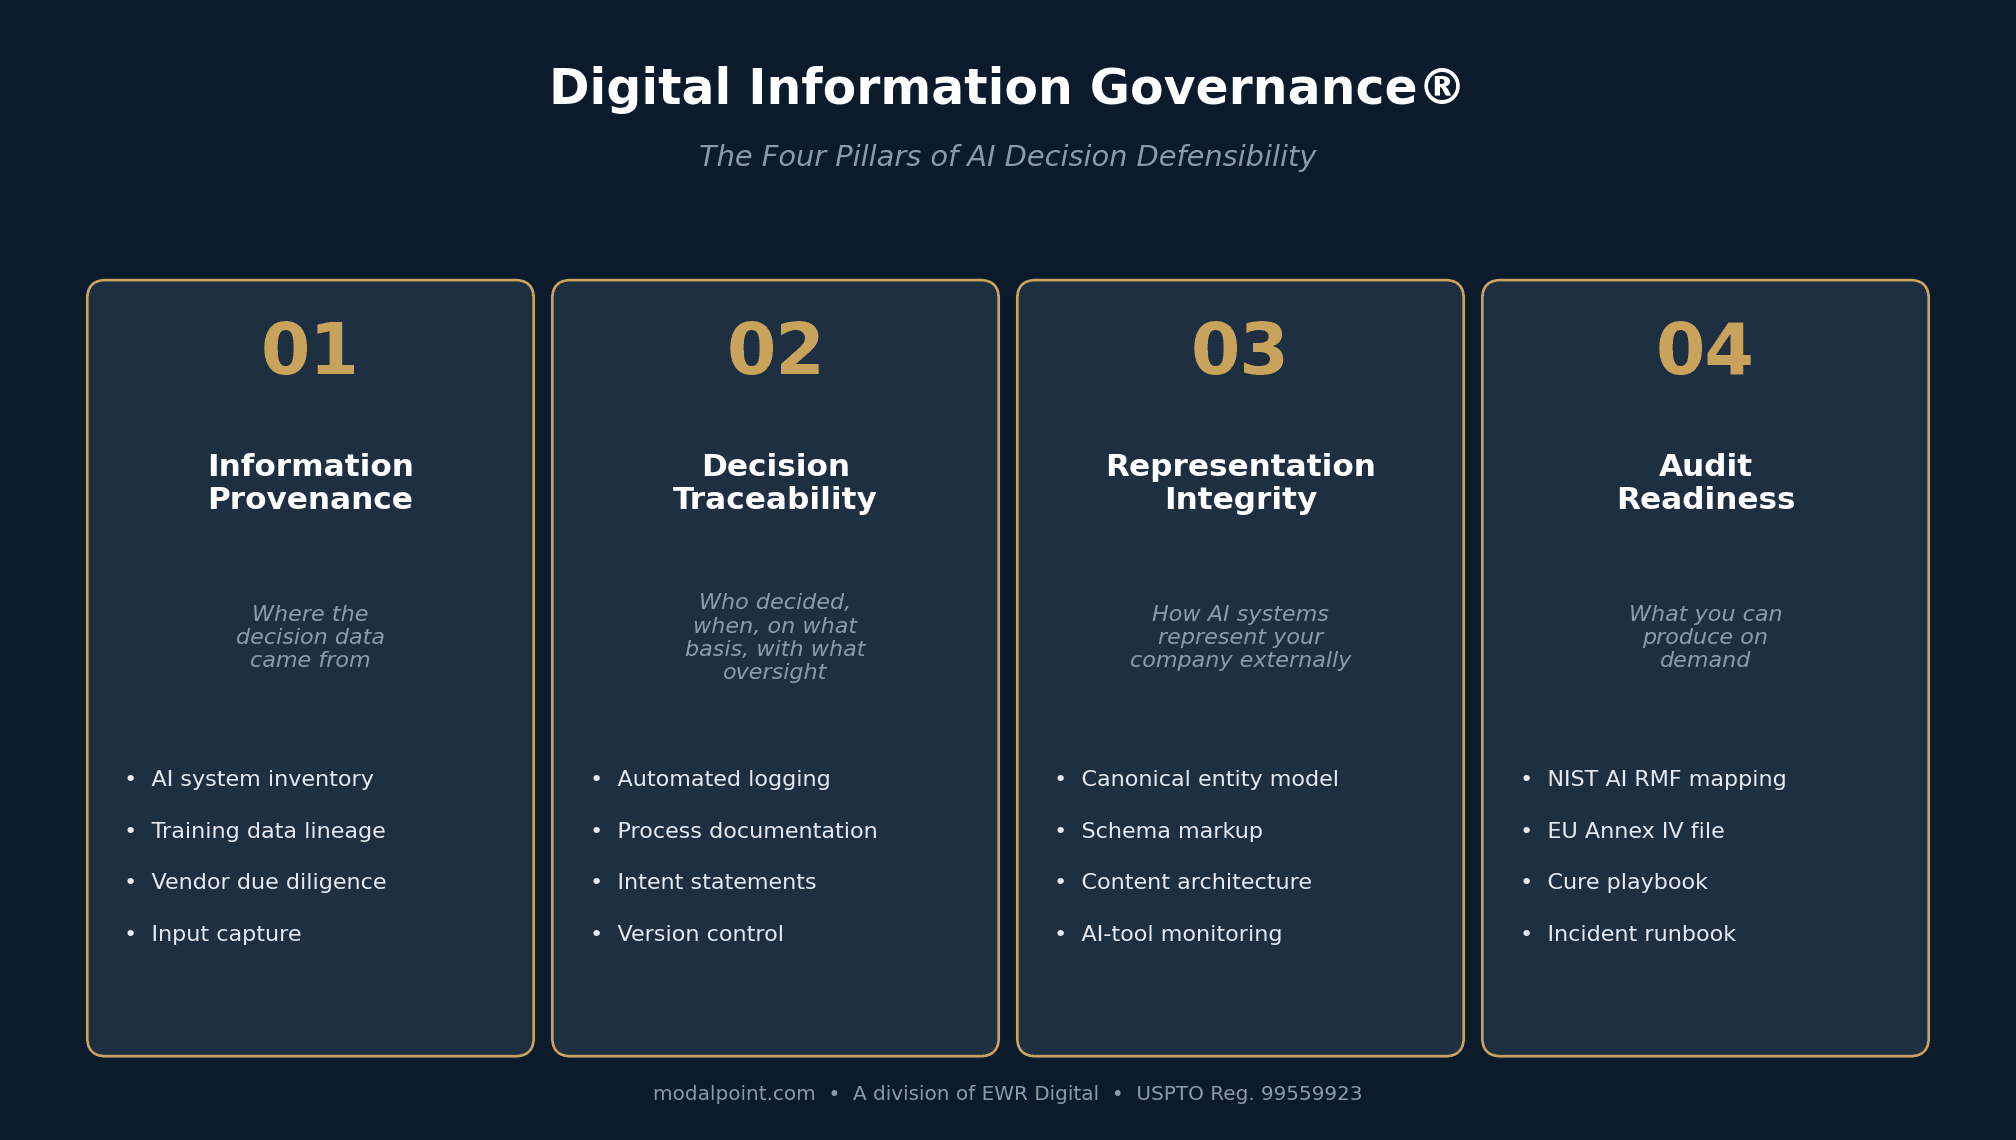
Here is the part most vendors miss. These four regimes are not four separate compliance projects. They share the same spine: documented risk assessments, decision records that show who approved what and why, human-oversight checkpoints, and ongoing monitoring. Build one NIST-aligned decision-record system and it produces the evidence an EU conformity file needs, the artifacts an ISO 42001 auditor asks for, and the reasonable-care record that earns the TRAIGA safe harbor, all at once. That is the whole idea behind AI decision governance. Not sure where you stand? Our AI Compliance Checker maps your current controls to each of these frameworks in a few minutes.
Frequently asked questions
Does the EU AI Act apply to US companies?
Yes. The EU AI Act applies to any provider or deployer whose AI system output is used inside the EU, no matter where the company is based. Prohibited-practice violations reach up to 35 million euros or 7% of global annual turnover, and the core high-risk obligations begin on August 2, 2026.
Does Texas TRAIGA require a third-party AI audit?
No. TRAIGA (HB 149) is a safe-harbor incentive, not an audit mandate. Substantial compliance with the NIST AI Risk Management Framework earns a rebuttable presumption of reasonable care. Civil penalties run from 10,000 to 12,000 dollars per curable violation up to 80,000 to 200,000 dollars per uncurable violation, and only the Texas Attorney General can enforce it, after a 60-day cure period.
Which AI regulations actually require an independent audit?
Very few. New York City Local Law 144 is the clearest US example: it requires an independent bias audit of automated hiring tools before use, renewed annually and posted publicly. The EU AI Act requires a notified-body conformity assessment for high-risk systems. NIST AI RMF, ISO 42001, and TRAIGA do not require a third-party audit.
What is the difference between NIST AI RMF and ISO 42001?
NIST AI RMF is a voluntary US framework of practices built on four functions: Govern, Map, Measure, and Manage. ISO/IEC 42001 is an international management-system standard you can be formally certified against by an accredited body. NIST tells you what good governance looks like; ISO 42001 gives you a certificate that proves it.
Do I need a separate compliance program for each framework?
No. All four share the same spine: documented risk assessments, decision records, human-oversight checkpoints, and ongoing monitoring. One NIST-aligned decision-record system produces the evidence that satisfies EU AI Act conformity files, ISO 42001 audits, and the TRAIGA safe harbor at the same time.
Talk to ModalPoint
A 20-minute call to see if ModalPoint is the right firm and whether the timing makes sense. No obligation either way.