Shadow AI Exposure Assessment for Energy
Find the unsanctioned AI already in use, classify what it exposes, and get a defensible 60-day remediation plan. Three-week diagnostic, from $2,500.
95%
of EHS+ teams use unapproved AI
CORITY INSIGHTS ’25 →
Find the AI your team is using that you didn’t authorize.
A 3-week diagnostic that surfaces unsanctioned AI usage across your organization, classifies the exposure, and produces a defensible 60-day remediation plan. $2,500.
Goldman 10KSB
OTC 2026
Texas AI Council
NIST AI CoI
Most operators we talk to assume they have an AI policy in place. They’ve issued the memo. They’ve stood up the sanctioned tool. They’ve mandated training.
Then we run the assessment. And we find:
- A senior engineer pasting AFE economics into ChatGPT on a personal account because the sanctioned tool times out on documents over 50 pages.
- A finance team running deal-memo summarization through Claude on the side because the corporate Copilot license doesn’t include the model they need.
- A field operations lead routing inspection photos through a third-party vision API for analysis — outside any logged workflow, on a personal Stripe-funded developer account.
- An entire procurement function quietly using Cursor to draft contract language with vendor PII embedded in the prompts.
This is not a security failure. It’s a signal that the sanctioned tool isn’t good enough, and the people whose work matters route around it. You don’t have a governance problem. You have a tool-quality problem creating a governance problem.
That’s what the Shadow AI Exposure Assessment surfaces, classifies, and gives you a defensible plan to fix.
→ Schedule a 30-minute discovery call
What We Look For
The assessment hunts for unsanctioned AI usage across six categories where exposure tends to concentrate:
- Browser-based generative AI on personal accounts. ChatGPT, Claude, Gemini, Perplexity — running through
chat.openai.comandclaude.aion accounts the IT team didn’t issue. - AI-augmented developer tooling. Cursor, Windsurf, GitHub Copilot configurations, Anthropic Claude Code, and AI-extended IDEs in dev workflows that weren’t approved at the function level.
- AI-in-Slack-or-Teams. Glean, ChatGPT-in-Slack, custom GPT integrations posted to channels, AI summarization plugins that received contract-level data.
- Spreadsheet and document agents. Excel
=GPT()integrations, Google Docs Smart Compose with custom training, formula-resolving AI add-ons, AI-PDF analysis tools running on regulated documents. - Field workflow API usage. Vision-recognition APIs analyzing physical assets, transcription services in inspection workflows, mobile AI tools used by field engineers and offline ops staff.
- Marketing and external-communications AI. Content tools, AI-image generators, brand-language assistants — running on assets that go to public regulators, investors, and customers.
For each category, we identify:
– Who is using it (role, function, level of seniority)
– What data class is being processed (employee, customer, contractual, regulated, classified, public)
– Why they routed around the sanctioned tool (capability gap, access friction, training gap, deliberate workaround)
– What downstream artifact the AI output ended up in (a memo? a regulator filing? a PR pitch? a customer email?)
What You Get
After three weeks, you receive a single binder containing:
1. Shadow AI Inventory
Every unsanctioned AI tool we identified, mapped to the user, function, and data class. Sorted by exposure severity.
2. Sanctioned-Tool Gap Analysis
For each shadow AI use case, the specific reason the sanctioned tool didn’t satisfy the user’s need. This is the part most clients didn’t realize they were missing.
3. Risk Classification Matrix
Each finding rated against four lenses: regulatory exposure (TRAIGA, EU AI Act, NIST AI RMF Critical Infrastructure Profile), data-protection exposure (GDPR, CCPA, contractual NDAs), reputational exposure (where outputs ended up that you’d rather not defend), and operational exposure (workflow continuity if the shadow tool is shut down).
4. 60-Day Remediation Roadmap
Specific, sequenced actions: which shadow uses to sanction, which to replace, which to ban, and what’s needed to upgrade the sanctioned-tool tier to close the capability gap that drove the workaround.
5. Discovery-Call-Ready Documentation
A separate executive brief sized for board and audit-committee distribution. Defensible language. No surprises.
What This Is Not
- Not a security audit. We don’t pen-test the sanctioned tools. We don’t crawl the firewall logs. SOC2 auditors do that.
- Not a tool ban. The fastest way to push shadow AI deeper underground is to issue a memo telling the team to stop. The assessment surfaces why people routed around the policy — so the next policy works.
- Not a $50,000 big-bang governance project. That’s the Texas Ready or Cross-Border Binder — for organizations that already know their exposure. The Shadow AI Exposure Assessment is for the operators who don’t yet know.
- Not theoretical. The deliverable lists specific tools, specific users, specific data classes. The remediation roadmap is sequenced and testable. Every finding has a citation.
Pricing & Scope
$2,500 flat fee. Three weeks. Five to ten stakeholder interviews (1:1, confidential, off the record). Documentation review. Sanctioned-tool capability inventory. Final binder + executive brief delivered as a single PDF + a 90-minute walkthrough.
If the assessment surfaces issues that warrant the full Texas Ready or Cross-Border Binder programs, the $2,500 is credited toward that engagement.
Who Should Run This
The Shadow AI Exposure Assessment is built for the operator who knows AI is happening informally inside their organization but doesn’t yet know how to map the exposure. Most often, this is:
- A COO or VP Operations at a $50M–$300M energy operator, industrial firm, or PE-backed portfolio company who suspects unsanctioned AI usage but doesn’t have a credible inventory yet
- A General Counsel or Chief Compliance Officer facing TRAIGA September 1, 2026 enforcement (or EU AI Act August 2, 2026 high-risk obligations) who needs to know what’s actually happening before policy goes into effect
- A PE Operating Partner or MD running portfolio-company AI risk diligence — at the GP or portfolio level — who needs a short, repeatable assessment to deploy across the portfolio
Two things have to be true for the assessment to be a fit:
- You have 5–10 senior individuals across operations, finance, IT, marketing, and engineering whose work involves making decisions or producing artifacts that have regulatory, contractual, or reputational consequences. (Below 5 stakeholders, the assessment is a phone call. Above 100, it’s a different program.)
- You’re willing to let those individuals talk to ModalPoint off the record, with no IT-team supervision, with explicit safe-harbor for what they admit to using. Without that condition, the assessment surfaces nothing useful.
How It Connects to the Rest of the ModalPoint Practice
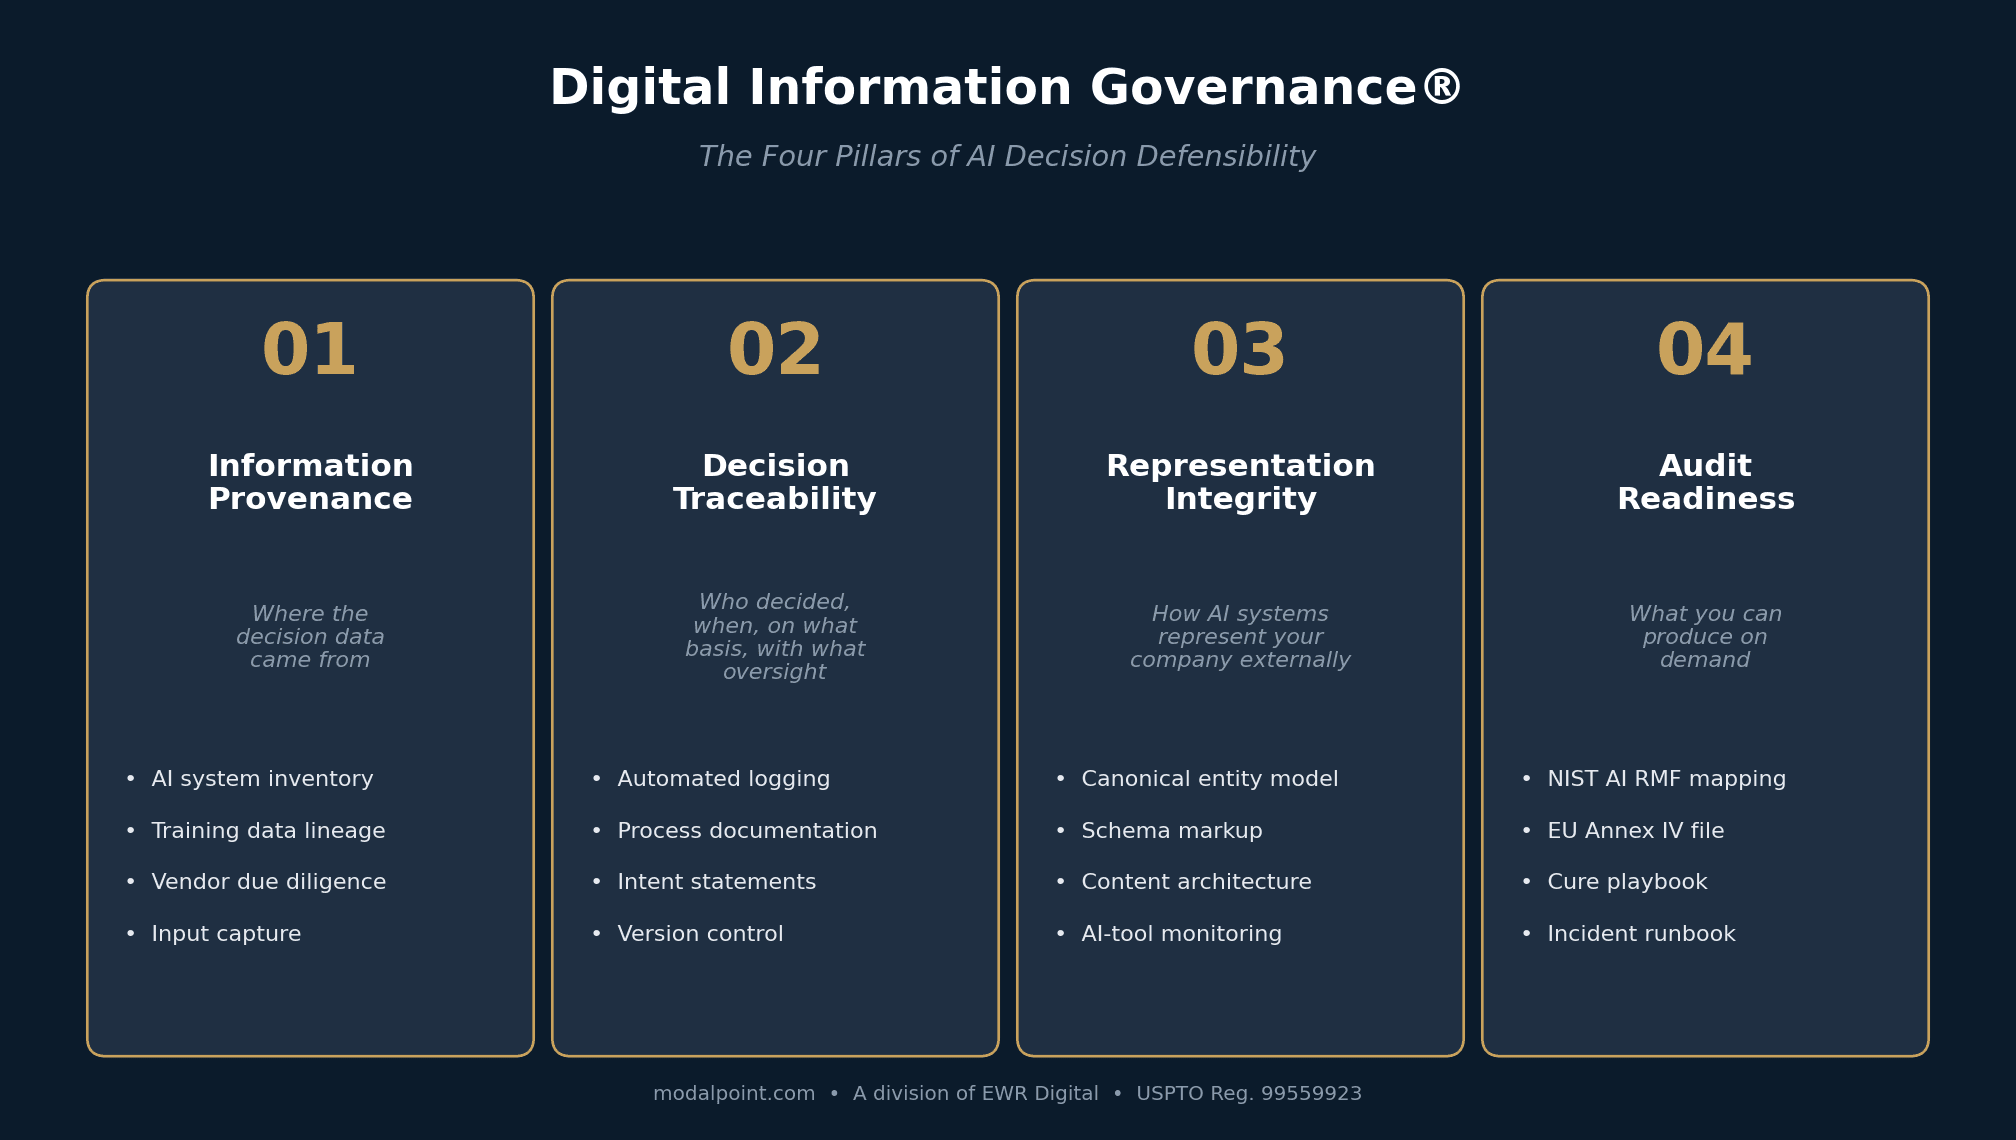
The Shadow AI Exposure Assessment is the entry tier of a four-tier engagement ladder, all built on the Digital Information Governance® framework:
| Tier | Engagement | Investment | Outcome |
|---|---|---|---|
| Tier 0 | Shadow AI Exposure Assessment | $2,500 / 3 weeks | Inventory + gap analysis + 60-day roadmap |
| Tier 1 | Texas Ready | 4–6 weeks | NIST AI RMF mapping, AI inventory, TRAIGA cure playbook |
| Tier 2 | Cross-Border Governance Binder | 8–12 weeks | All nine DIG artifacts: TRAIGA + EU AI Act + NIST + ISO 42001 |
| Tier 3 | Governance-as-a-Service | Monthly retainer | Drift monitoring, regulatory watch, incident response standby |
The Shadow AI Exposure Assessment is designed to be a complete-and-shippable deliverable on its own. Most operators run it, take the binder, and act on the roadmap themselves. About one in three return to commission the deeper Tier 1 or Tier 2 work after the initial assessment surfaces exposure that warrants the full binder.
Schedule a Discovery Call
A 30-minute discovery call to confirm fit, scope the stakeholder list, and answer questions about the methodology. No prep needed. No commitment. Held under NDA on request.
Or if you’d rather see the broader practice first:
- What is Digital Information Governance®? — the framework all four tiers are built on
- What We Do — the Tier 1 / Tier 2 / Tier 3 program details
- Who We Are — about ModalPoint and Matthew Bertram
Based in Houston, Texas. ModalPoint is the AI Decision Governance practice for regulated industries — built on 26 years of energy commercialization advisory through EWR Digital. Matthew Bertram is President of ModalPoint, CEO of EWR Digital, member of NIST’s Cyber AI Profile and Zero Trust Communities of Interest, Goldman Sachs 10,000 Small Businesses graduate (April 2026), and moderator of the Ericsson AI panel at Offshore Technology Conference 2026 (May 4).
Find what’s already running inside your organization.
/ Who you're engaging with
A Houston-based AI decision governance practice. Built by operators, sharpened on regulated AI.
/ Practice
/ Credentials & affiliations
NISTCyber AI · Zero Trust CoI
TexasHB 149 / TRAIGA active
Goldman10KSB graduate, Apr 2026
TAMUCorps of Cadets alumnus
IAPPAIGP candidate, Q3 2026
OTC 26Moderator, Ericsson AI panel
/ Connect
Frequently asked questions
How is this different from a security audit?+
Is the $2,500 credited toward the larger Tier 1 or Tier 2 engagements?+
Will my team's admissions be confidential?+
How long does the assessment take?+
Does ModalPoint sell the AI tools we should use?+
Talk to ModalPoint
A 30-minute call to see if ModalPoint is the right firm and whether the timing makes sense. No obligation either way.